
Purpose-Built Key Management
for Authority Infrastructure
Stronghold-KMS governs authority keys for any regulated infrastructure — blockchain nodes, validators, PKI systems, and signing infrastructure. First deployed for Canton networks, built for any system that depends on authoritative key control.
Canton · Blockchain Validators · Certificate Authorities · Signing Infrastructure
System-Level Keys
Wallet keys move assets. System-level keys protect the network itself. In Canton, security isn't just about asset custody — it's about trust in every node, every transaction, and every rule embedded in the system. System-level keys power encrypted state sharing, consensus, and operational logic. And these same patterns apply across any infrastructure where authority keys govern trust.

Built for Any Authority Key
Canton is the first deployment. Stronghold-KMS is designed around a principle, not a product: any system that depends on authority keys for its integrity deserves the same level of controlled custody.
One architecture. Any authority key system.
The same custody model that governs Canton node keys applies wherever authority keys underpin infrastructure trust. The key management problem is universal; only the key types change.
Stronghold-KMS separates the policy engine, the HSM integration layer, and the key lifecycle logic — so onboarding a new key type is a configuration exercise, not a re-architecture.


Infrastructure Trust Is Non-Negotiable
Authority key compromise doesn't trigger a fraud alert. It silently erodes the trust that makes regulated infrastructure function.

Traditional security protects keys. Modern systems must govern authority.
Why Authority Keys Need Purpose-Built Management
Authority key systems operate under a distinct trust model. Key management must align with participant topology, governance scope, and the operational realities of the system being protected.
Stronghold-KMS is not a tool, it is a control infrastructure.
Built for Authority Keys. Built for Resilience.
Every capability is designed around the operational realities of authority key systems — governed key lifecycle, policy-mediated access, and sovereign custody.
Zero Trust In Action
Your keys. Your policies. Even MPCH has no access.
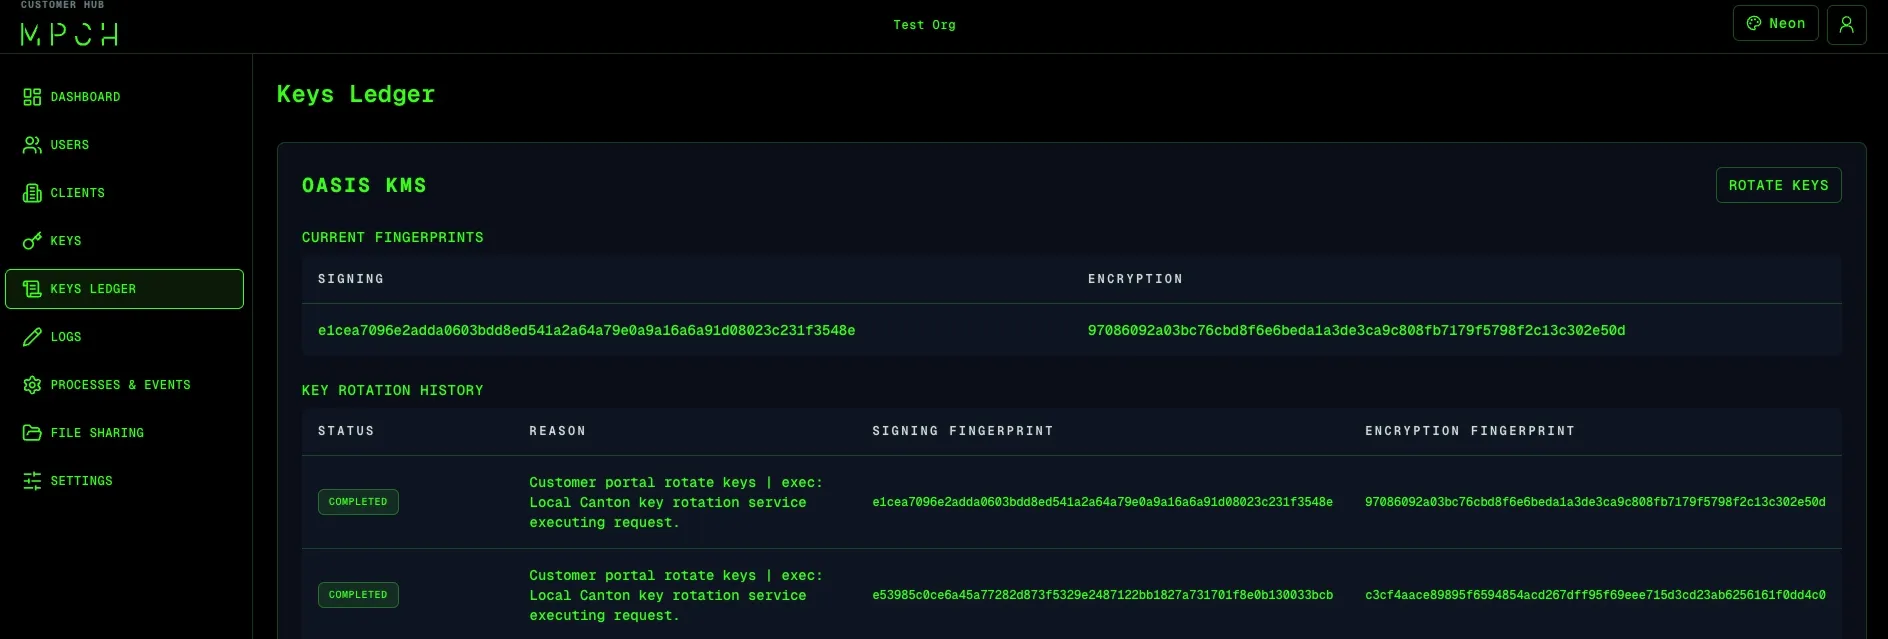 Keys Ledger
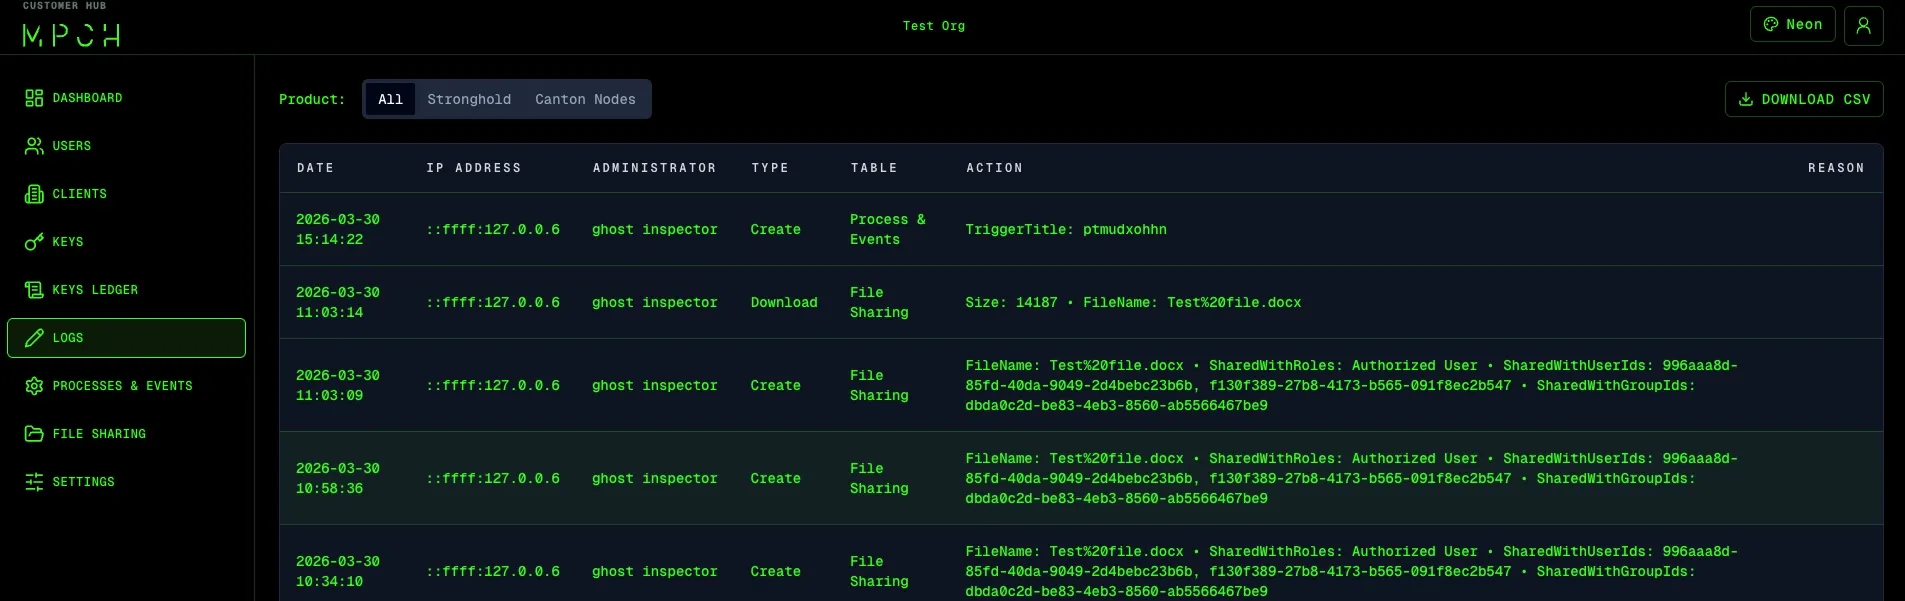 Audit Logs